PVYvault: Enterprise-level password and credential management for enhanced security.
PVYvault, available at our Appstore, is not just another password manager. It's a PriVacY-first, zero-knowledge, root-less credential management platform that is architecturally designed to eliminate the attack surfaces that plague conventional password managers. And its very smart and user friendly.
All data in PVYvault is encrypted at rest and in transit. The cryptographic architecture employs three encryption schemes:
- Simple Symmetric Encryption — AES-GCM with randomly generated keys for ephemeral encryption
- Password-Based Encryption — PBKDF2 key derivation (per RFC 2898) combined with AES-GCM, using the user's master password
- Shared-Key Encryption — RSA public-key encryption (per RFC 7516 / JSON Web Encryption) for securely sharing vault items between multiple users without sharing a common password
The database itself is a PostgreSQL instance where entries are not only hashed but encrypted. Even with physical root access, stored items cannot be queried — only the table structure can be retrieved. Documents and attachments are stored in a special mounted encrypted volume (Encrypted Disk-Image) for each deployment.
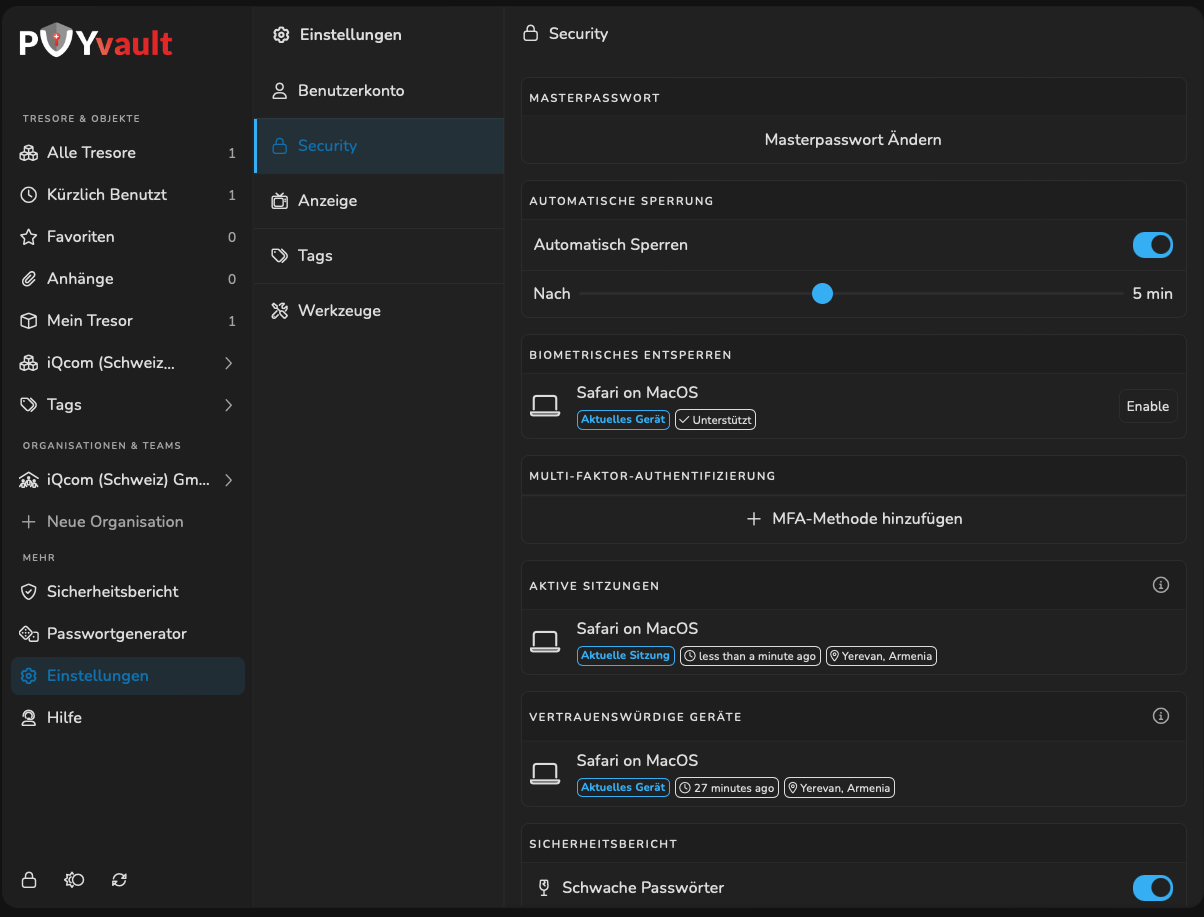
We cover the Architectural and Security Design of PVYvault, Usability and few example other Password Manager failing, a short preview of the PVYvault Extension, PVYvault Enterprise Admin Portal, and highlight the differences in Deployment Methods against the known ones.